01
AI Inventory
Register external agents, applications, models, tools, owners, and deployment status.
 Sierra HealthTech Innovations
External healthcare AI trust infrastructure
External healthcare AI trust infrastructure
One secure way for outside AI to identify itself, receive permission, access healthcare tools and data, execute approved work, and prove what happened.
Licensed Anchor Point distributor for MedTech · MedTech is the first market
Sierra // External AI security
Illustrative platform view
Known agents
Identified
Scoped access
Purpose bound
Trusted events
Evidence created
Live policy decisions
Identity · Purpose · PermissionCase Logistics Agent
inventory.read
Authorization Agent
document.submit
Unknown vendor agent
patient.clinical.read
Trust chain
Decision evidence
Owner, model, tool, purpose, policy, decision, and result recorded as one trusted event.
The cross-organization problem
Yet their systems need to work together. Sierra establishes the trusted identity, permission, connection, and evidence that lets an outside AI actor participate in a healthcare workflow.
Identify the agent, application, model, owner, operator, and tools behind every request.
Separate identity from authorization, then evaluate purpose and minimum-necessary access at runtime.
Preserve the policy, decision, result, provenance, and risk context as an auditable event.
The Sierra trust network
Every request is tied to an organization, human authority, agent, purpose, permission, and destination before an approved action reaches healthcare.
Explore the Sierra GatewayExternal ecosystem
Sierra trust boundary
Discover
Identify
Authorize
Inspect
Enforce
Prove
Healthcare infrastructure
Discover
Identify
Authorize
Inspect
Enforce
Execute
Prove
External healthcare AI infrastructure
Security is the admission requirement. Sierra combines it with trusted connectivity and governed execution across organizational boundaries.
Register external agents, applications, models, tools, owners, and deployment status.
Verify the chain of authority from organization and operator to agent, model, and tool.
Route external AI activity through one healthcare-specific trust and enforcement boundary.
Evaluate purpose, permissions, data class, facility, and workflow before every action.
Inspect behavior for prompt injection, tool misuse, data leakage, and unexpected destinations.
Create evidence of who acted, why, under which policy, and with what result.
Healthcare policy at runtime
An authenticated agent still needs a valid purpose, permitted data, approved tools, an authorized destination, and the right human or organization behind it. Sierra evaluates that context for every action.
Minimum necessary access
Prefer short-lived, scoped authorization for the current workflow over persistent vendor credentials.
Allow
Execute an action that satisfies identity, purpose, permission, and policy.
Deny
Stop an action that falls outside the approved workflow or trust chain.
Redact
Remove sensitive fields before the request reaches its destination.
Transform
Modify a request so it conforms to the receiving organization’s policy.
Require approval
Pause higher-risk activity for a named human decision-maker.
Trusted healthcare events
Preserve who acted, what agent and model were used, why the action occurred, which data and tools were involved, which policy decided it, and what result followed.
Technology partnership
As a licensed Anchor Point distributor for MedTech, Sierra uses Anchor Point’s identity, policy, security, observability, and controlled-execution foundation at the trust boundary around healthcare’s third-party ecosystem.
Sierra for independent MedTech
Sierra also helps independent MedTech organizations deploy governed agents for cases, purchase orders, inventory, authorization, DME, CRM, contracts, and knowledge — with the gateway operating beneath the workflow.
Partner product
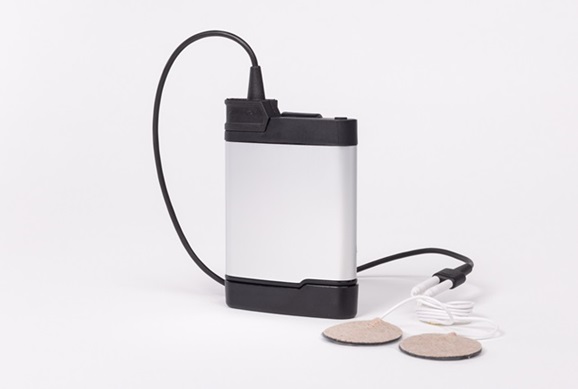
Manufactured by Theragen · Distributed and supported by Sierra
A prescription wearable bone growth stimulator supported through Sierra’s distribution, onboarding, insurance coordination, and patient-service operations.
Sierra is designed for AI systems operated outside a healthcare organization — including agents and applications from manufacturers, distributors, representatives, DME suppliers, and other third parties.
No. Sierra treats identity and authorization separately. A verified agent must still have an approved purpose, limited permissions, permitted data, and an authorized destination for each action.
The gateway can allow, deny, redact, or transform a request. It can also pause execution and require a named human to approve the action.
Each action can produce a trusted event that records the actor, owner, model, tool, purpose, permission, policy, decision, result, provenance, and risk context.
Yes. Sierra applies the same governed foundation to practical MedTech agents for cases, purchase orders, inventory, authorization, DME, CRM, contracts, and knowledge.
Establish the trust boundary
Explore how Sierra can identify external AI actors, enforce purpose-bound access, and preserve evidence across healthcare connections.
Request a platform briefing